
- Published
- Mar 24, 2026
- Updated
- Nov 4, 2026
- Reading time
- 24 min read
ads.txt and sellers.json Disagree: An Investigation Checklist
Resolve seller-file conflicts with checks for DIRECT, RESELLER, manager domains, app-ads.txt discovery, redirects, and safe supply-path cleanup.
In this guide (14 sections)
Your monetization partner supplies an ads.txt file containing DIRECT entries. You look up the seller IDs and find the partner listed as INTERMEDIARY in sellers.json. Is the file wrong? Should you remove the entries? Does declaring a manager settle the issue?
If the missing identity starts in a DV360 export, use the buyer report and seller-lookup workflow before assuming the export contains a complete supply chain.
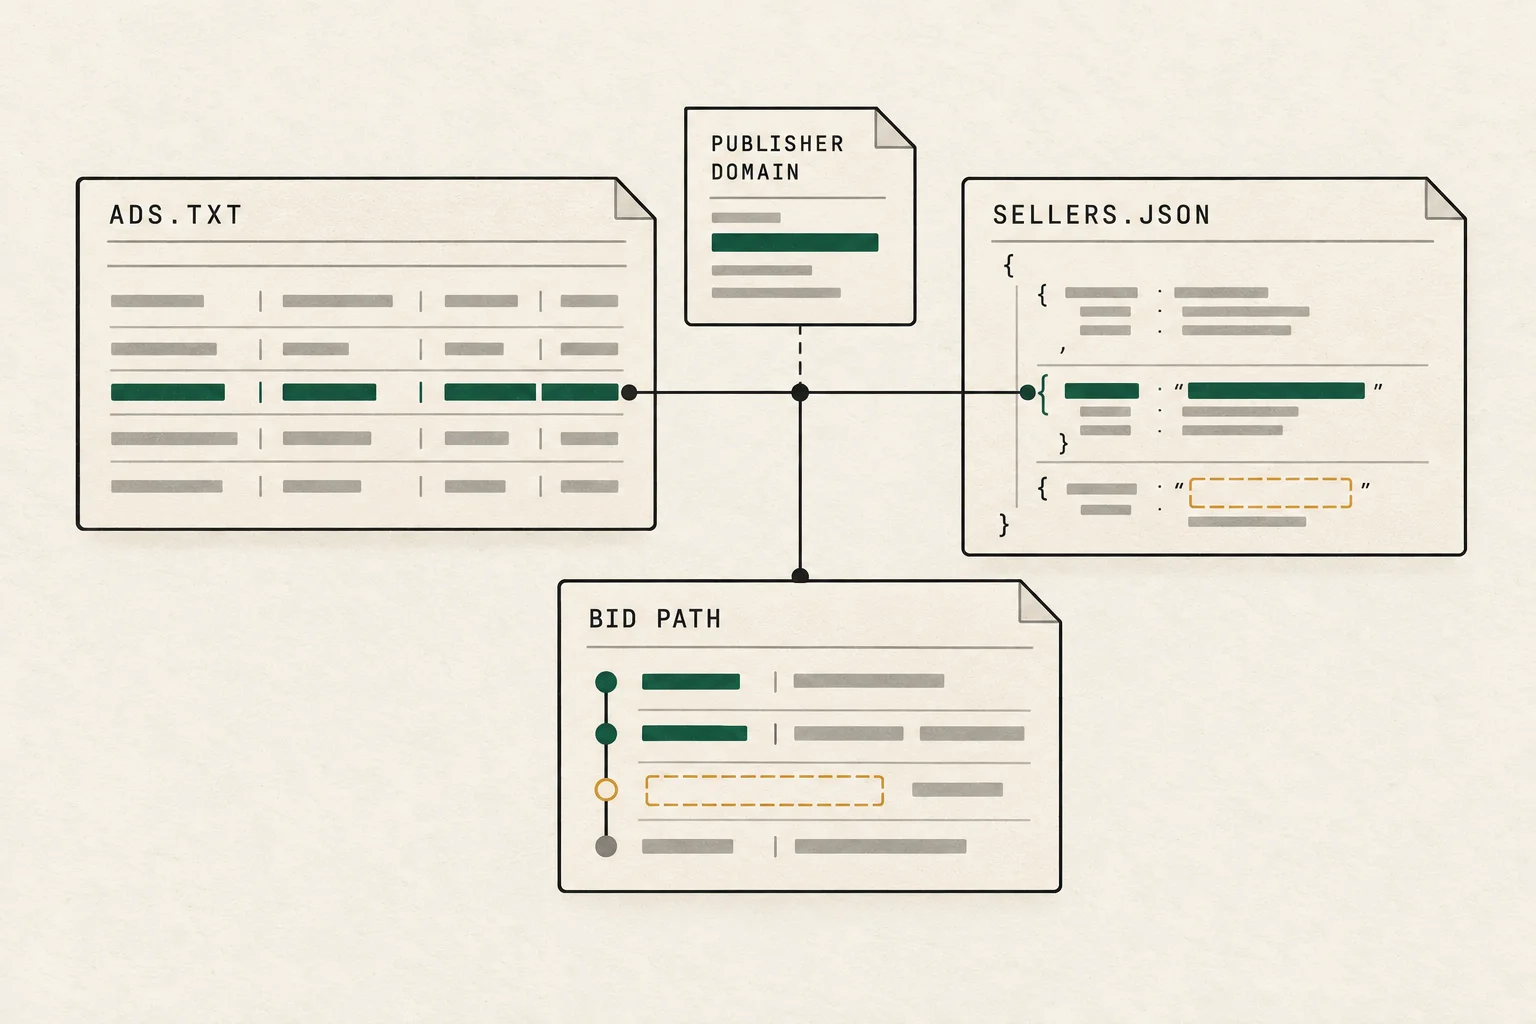
The answer starts with three different records: the publisher's authorization, the advertising system's seller identity, and the path declared in an actual bid. This guide shows how to reconcile them, investigate unfamiliar sellers, and clean up authorizations without guessing about revenue.
A publisher described this exact DIRECT versus INTERMEDIARY problem on r/adops, including a MANAGERDOMAIN declaration. The thread establishes the question. The technical distinctions below come from IAB Tech Lab's specifications and implementation guidance.
What each file can tell you#
| Evidence | Where it comes from | Question it answers | What it does not establish |
|---|---|---|---|
| ads.txt | Website publisher | Which advertising-system accounts are authorized to sell this inventory? | Which path actually transacted an impression |
| app-ads.txt | App developer's declared website | Which accounts are authorized for the relevant app inventory? | Whether the app identity in every bid is truthful |
| sellers.json | Advertising system | Which entity is represented by an account ID, and what is its seller type? | Authorization from every publisher named or represented |
| SupplyChain object, or schain | Individual bid request | Which sellers are declared in this transaction path? | Independent proof that every declaration is accurate |
| Delivery evidence | Measurement and delivery records | What happened to the purchased exposure? | Public authorization by itself |
IAB Tech Lab's ads.txt overview describes the authorization mechanism for websites and apps. Its sellers.json overview explains the complementary identity and transaction-path roles.
A clean set of files reduces uncertainty about the declared selling relationship. It does not certify a human audience, viewability, correct geography, attention, or commercial value. Those require separate checks such as invalid traffic analysis and campaign delivery verification.
Compare authorization with the reported seller path
ads.txt, sellers.json and a supply-chain record describe different parts of a transaction. Discuss the specific seller evidence available.
Discuss measurement optionsA short inquiry to scope relevant options; no campaign access is needed.
DIRECT and INTERMEDIARY are not opposite values in one field#
The most common shortcut is to compare the two labels as though they used the same vocabulary. They describe related but different relationships.
In the ads.txt 1.1 specification, DIRECT concerns the publisher's control of the named account in the specified advertising system. RESELLER describes authorization of another entity's account for resale. The relationship belongs to that account and system, not to the partner's marketing description.
The sellers.json specification classifies the seller account as PUBLISHER, INTERMEDIARY, or BOTH. Its definitions consider inventory ownership and payment relationships. BOTH means the account can represent owned and other inventory; it is not blanket proof of a correct DIRECT declaration on every property.
A mismatch is therefore a reason to inspect the account, ownership, payment, and management arrangement. Do not automatically accuse a partner of fraud. Equally, do not accept “we are your direct partner” as sufficient justification for every DIRECT line.
OWNERDOMAIN and MANAGERDOMAIN add context
OWNERDOMAIN identifies the business entity that owns the property. MANAGERDOMAIN identifies an applicable primary or exclusive monetization manager, with country scope where declared.
The ads.txt 1.1 implementation guide makes an important distinction: a manager can be the most direct purchasing path from a supply-path perspective even when an exchange account is correctly declared RESELLER. “Most direct path” does not mean every row must contain the literal value DIRECT.
A MANAGERDOMAIN line does not rewrite the account controller or make unrelated seller IDs correct. Check it alongside seller domains, the applicable country, and the actual path. Ask the manager to show which documented scenario represents the integration.
A worked investigation of one suspicious line#
The following is an original hypothetical case using reserved example domains. It illustrates the questions to ask; it is not a claim about a real publisher or vendor.
Suppose news.example belongs to News Group, whose business domain is newsgroup.example. The publisher appoints manager.example to manage monetization. A file contains:
OWNERDOMAIN=newsgroup.example
MANAGERDOMAIN=manager.example
exchange.example, seat-700, DIRECT
The exchange's seller record identifies seat-700 as Manager Company, domain manager.example, type INTERMEDIARY.
Start with the account, not the label. Ask who owns and controls seat-700, who is paid by the exchange, and what seller account represents News Group at the manager. Request the relevant current bid-path evidence and the partner's implementation rationale.
If the account is the manager's resale account, declaring the manager does not by itself justify changing its ownership story. A documented managed path might instead distinguish the publisher's account at the manager from the manager's resale account at the exchange. Resolve the specific structure against the standards and the exchange's integration guidance.
Your resolution record should state:
| Question | Evidence to retain |
|---|---|
| Which entity owns the inventory? | Publisher confirmation and owner-domain declaration |
| Which entity controls this exchange account? | Account and contractual confirmation from the relevant parties |
| Who receives payment at this step? | Partner confirmation of the payment relationship |
| Does the seller domain match owner or declared manager? | Dated seller record and applicable declarations |
| Which path appears in bids? | Authorized, redacted bid samples with timestamps |
| What needs correcting? | Exact row, seller record, or path declaration and responsible owner |
Do not “fix” the warning by changing the label until the warning disappears. Fix the declaration that misrepresents the established relationship, then revalidate the same observed path.
Read the actual bid path in the correct order#
The OpenRTB SupplyChain specification defines ordered nodes. In a complete chain, the first node represents the initial advertising system and seller associated with the inventory owner, and the last represents the entity sending the request. In an incomplete chain, the first node is only the first known node.
For each relevant node, record:
asi: the advertising-system identifier.sid: the seller account within that system.- Seller identity resolved from that system's sellers.json.
- The declared path's completeness and applicable version.
- The authorization and relationship relevant to that account and inventory.
The same seller ID string on two systems is not necessarily the same account. Always join the pair of system domain and seller ID. Do not drop leading zeros or other meaningful account-ID characters.
A completeness flag is a declaration, not independent validation. If a chain says it is complete but the expected publisher-to-manager relationship is unexplained, record the inconsistency. If it says incomplete, retain that limit rather than describing the file lookup as a complete supply audit.
Use the current specification's rules for your integration. Distribution, inventory-sharing, and delegated monetization arrangements can require additional context. Do not apply a simplistic one-hop rule to every CTV app or attempt to infer a payment chain from a screenshot of an exchange name.
Why your company might appear in an unfamiliar sellers.json#
In a September 2026 discussion, a company asked why businesses it had never worked with were publishing its identity in seller files. The discussion contains suggested explanations, not verified findings about those companies.
Treat the listing as a claim to investigate. It could involve an indirect arrangement, an old integration, mistaken identity, stale account metadata, or a misrepresentation. The public record alone cannot distinguish these possibilities.
Preserve the evidence first
Save the file URL, fetch time, HTTP status, exact seller ID, name, domain, type, and any confidentiality or passthrough fields. Preserve the complete response privately so the context is recoverable even if the public file changes.
Check whether the domain identifies your legal entity rather than a similarly named business. Compare against historic partner records and acquisitions. An internal team may know a relationship that the person spotting the listing does not.
Ask the publishing system to explain the account
Request the account controller, onboarding relationship, and reason your entity is identified. Ask whether the entry is active, whether it has transacted inventory associated with your property, and which upstream relationship supports the declaration.
If the publisher and account owner are different entities, ask for the relevant authorized chain. Do not assume an unfamiliar listing grants authority over your property. Likewise, absence from your ads.txt should lead to the applicable authorization check, including relevant app or distribution rules, rather than an instant public accusation.
Google Ad Manager's seller-information guidance provides a concrete platform example: a seller record represents the paid entity and may cover multiple properties, while intermediary accounts have distinct disclosure requirements. Confirm how the specific publishing system represents the account involved in your case.
Record an outcome that another person can review
Useful outcomes include verified indirect relationship, corrected identity, obsolete entry removed, or unresolved account claim. Record what evidence supports the outcome and who confirmed it. If unresolved activity presents a buying risk, apply your documented escalation policy and preserve the distinction between uncertainty and proven abuse.
Should you remove RESELLER entries when you already have DIRECT?#
A publisher with a large ads.txt file asked this in March 2026. The presence of two entries naming the same exchange does not tell you whether they represent duplicate access, separate accounts, different integrations, or different demand relationships.
Public declarations do not show revenue, fees, winning bids, or incrementality. You cannot calculate the commercial effect of removing an account by counting rows in the file.
Start an account-level inventory:
| Field | Why it matters |
|---|---|
| Advertising system and seller ID | Identifies the actual authorization under review |
| Responsible partner | Gives the row an accountable owner |
| Relationship and seller identity | Exposes discrepancies needing correction |
| Integration and deal usage | Finds where the account is used |
| Applicable property and geography | Prevents changes outside the intended scope |
| Recent requests, wins, and revenue | Indicates observed activity where data is available |
| Unique demand or obligations | Identifies contractual and commercial dependencies |
| Last validation and decision | Keeps cleanup evidence current |
If the integration is unused, obtain partner confirmation before removing authorization. If it is active, ask what would continue through the retained route and what might disappear. “Both use the same SSP” is not an answer about identical demand.
Use a reversible cleanup experiment
Choose a small, understood group of entries. Save the complete original file and exact proposed diff. Confirm who can restore it, and establish a review interval long enough to observe crawler refresh and relevant trading activity.
Monitor authorization errors, bid participation, fill, and net revenue at the affected inventory and account level where available. Compare against a suitable baseline and document other changes during the period. A market-wide demand shift can affect revenue independently of your file edit.
Removing authorization does not necessarily remove the partner's tag, wrapper configuration, contract, or bid traffic. Coordinate those separately. Do not leave an active integration making requests through a deliberately deauthorized account without a documented reason.
There is no universal waiting period that guarantees all buyers have refreshed their cached files. Confirm the affected systems' current crawl and enforcement behavior, then verify their observed status.
App and CTV checks that a website audit can miss#
For apps, begin with the store listing and developer website used for app-ads.txt discovery. A correctly formatted file on an unrelated website does not establish that buyers can discover it for the app in question.
IAB Tech Lab's app-ads.txt materials describe the extension for mobile and CTV distribution. When investigating an app, record the store identifier, app identity in the bid, developer link, fetched authorization URL, and redirects.
Do not assume every inventory-sharing relationship is a MANAGERDOMAIN relationship. The relevant declaration and bid fields depend on the distribution arrangement. Ask which specification mechanism applies and retain the evidence connecting the app, rights holder, and selling accounts.
Once authorization is understood, investigate playback and counting separately. SSAI measurement and CTV impression reconciliation cover why two partners can count different events even when the declared supply path is legitimate.
Inventory-sharing authorization: join the app, partner file and request#
An older public integration question describes an app owner authorizing another business to sell a particular ad unit. The poster had both an INVENTORYPARTNERDOMAIN declaration and reseller rows, and asked whether file configuration or OpenRTB parameters could explain poor fill. Replies suggested other possible causes without establishing a diagnosis. The authorization question remains useful: does the received request actually use the relationship declared in the file?
First establish the business arrangement. IAB Tech Lab's inventory-sharing guidance concerns multiple entities with rights to sell portions of inventory. A payment described as a revenue share does not, by itself, establish that arrangement. The guidance distinguishes inventory sharing from a single inventory owner paying a content supplier a share of revenue; it also does not establish exclusive rights to particular programming. Ask the parties to confirm the actual selling rights before selecting a declaration.
Work through one request, not just a valid file
Use an authorized, redacted request received by the buyer, with its timestamp, alongside the declarations fetched for that app. The following is a recommended investigation sequence:
| Check | Evidence to join | Useful next action when it fails |
|---|---|---|
| Correct app | Store identifier, store URL and discovered developer website | Resolve which app and environment the request represents |
| Correct inventory owner | Agreement or partner confirmation covering the ad opportunity | Clarify who may originate the sale before editing declarations |
| Partner referral | App owner's app-ads.txt and the partner domain in the request | Correct a missing declaration, missing request value or wrong domain |
| Partner authorization | Referred domain's /ads.txt, advertising system and seller ID | Ask the responsible partner to correct its actual selling account |
| Seller identity | Same system and account in sellers.json | Resolve the entity/account mismatch rather than guessing from names |
| Payment path | Actual SupplyChain nodes and payment relationships | Investigate missing or unexplained payment participants separately |
The current ads.txt v1.1 specification says an inventory-partner referral is followed to the partner's ads.txt, rather than its app-ads.txt, and only one referral hop is consumed. A partner's file pointing to another partner does not authorize an unlimited recursive chain. This is a crawler-referral rule; it does not limit the number of SupplyChain payment nodes to one.
A complete hypothetical account example
Assume an app distributor and a content rights holder have confirmed that the rights holder may sell a defined portion of the app's inventory. The rights holder controls account 0041 at exchange.example. These domains, identifiers and relationships are hypothetical.
The app's discovered authorization file contains:
# https://distributor.example/app-ads.txt
INVENTORYPARTNERDOMAIN=rights-holder.example
The referred partner file contains:
# https://rights-holder.example/ads.txt
exchange.example, 0041, DIRECT
An abbreviated OpenRTB app object for the rights holder's opportunity contains:
{
  "app": {
    "bundle": "com.example.streamingapp",
    "storeurl": "https://store.example/apps/com.example.streamingapp",
    "publisher": { "id": "0041" },
    "inventorypartnerdomain": "rights-holder.example"
  }
}
This is an illustrative excerpt, not a complete bid request or a real store listing. Under the assumed integration, the authorization join is exchange.example plus 0041; the corresponding exchange seller record should identify the confirmed account entity. Preserve the leading zeros. A bid using 0042 requires its own account validation: a matching partner domain cannot repair the wrong seller ID.
The OpenRTB App definition places inventorypartnerdomain on the app object and points authorization to the partner domain's root ads.txt. Its Publisher definition makes publisher.id exchange-specific. For a real integration, confirm which received field the exchange documents for its authorization lookup rather than assuming a similarly named ID is interchangeable.
Check transport and adoption before deleting existing rows
Current OpenRTB uses app.inventorypartnerdomain or site.inventorypartnerdomain. The OpenRTB version history records promotion out of ext in November 2022. If a legacy integration sends an extension field, confirm the negotiated schema and what the recipient actually consumes; copying a sample from another version is insufficient. Inspect the outbound buyer request as well as the upstream request, because a value present before a handoff may be absent afterward.
For Google Ad Manager VAST requests, Google's inventory-sharing instructions use the ipd request parameter. Its value must match the declared inventory-partner domain; without it, that validation route does not occur. This Google tag parameter is not an instruction to add ipd to every native/banner OpenRTB request. Follow the transport used by the integration under investigation.
The same Google page warns that some DSPs may not validate IPD and advises retaining existing direct/reseller declarations during adoption. Verify the actual buyers' behavior before removing a working authorization route. Do not convert that documentation into a claim that every buyer currently supports, or rejects, the mechanism.
Finally, distinguish authorization from payment. Google's SupplyChain explanation excludes non-payment intermediaries from its chain, including inventory-sharing participants when they do not handle payment. A referral and a payment node answer different questions. Neither identifies a viewer, proves viewability, nor establishes that an impression was legitimate.
Record the exact failed join, response or buyer-reported rejection before making a correction. If authorization checks pass but fill remains low, investigate the request and auction separately; no file edit guarantees additional demand. For delivered events, the FMCG in-app measurement case demonstrates a separate distinction between traffic-quality filtering and duplicate counting. It is not evidence that this authorization configuration caused a customer's delivery gap.
AdMob finds the file, but the account details still do not match#
A developer asked why AdMob verification failed despite a reachable app-ads.txt file, after changing the developer website to Firebase Hosting. The question separates two checks that are easy to collapse: can a browser retrieve a seller line, and is AdMob retrieving the expected file for the linked app and account?
Do not start by buying another domain or removing a redirect. Google explicitly supports Firebase Hosting, including its web.app and firebaseapp.com subdomains. A supported host is not proof that every listing, response and seller ID is correct, but its name alone does not establish the cause of this error.
Follow the discovery chain before changing the file
Keep this small evidence table for the affected app. These are recommended investigation fields, not additional platform requirements.
| Boundary | Evidence to retain | What to investigate if it differs |
|---|---|---|
| App to store | Linked store listing and app identifier | Whether you are inspecting the same app that AdMob is verifying |
| Store to developer website | Website link on the public listing, with observation time | A saved console edit that is not yet visible publicly |
| Developer website to crawl URL | Exact app-ads.txt URL displayed in AdMob's detailed status | A different hostname or root path from the one you tested |
| Crawl URL to response | Redirect chain, final URL, status and plain-text body | An HTML fallback, challenge, stale empty response or missing file |
| Response to seller account | Personalized seller snippet copied from the intended AdMob account | Incorrect account ID, punctuation, whitespace or seller-system domain |
| Change to verification | Change time, last available crawl/status details and later observation | Whether the displayed result predates the correction |
AdMob's setup instructions derive discovery from the developer website's hostname, rather than expecting the store listing to contain the full file URL. They also define particular subdomain rules. For example, a listed www.publisher.example does not mean the crawler begins at that www hostname. Use the documented rules and the actual account-reported crawl URL instead of generalizing from whichever URL opens in your browser.
Google's troubleshooting page says the detailed status exposes the exact URL being crawled. That is a useful answer to “which URL is the crawler checking?” It does not show every downstream network or cache condition; preserve whatever status information is actually available rather than inventing a crawl receipt.
Test the app-ads.txt route, including redirects
A homepage redirect and an app-ads.txt redirect are different HTTP requests. A working homepage does not establish what the file route returns. Conversely, changing a homepage redirect without testing the file route may leave the relevant response untouched.
AdMob's setup guide explicitly permits redirects from the discovered file URL to other locations. “All redirects are invalid” is therefore too broad. Follow the exact file request through its final response. Review the applicable robots.txt rules at both the starting and destination hostnames, and ask the hosting administrator to check unsuccessful crawler requests. A successful request from your own browser does not rule out different CDN, security or cache handling for a crawler.
Google's crawlability guidance requires a successful HTTP status and parseable file content. An HTML error page carrying status 200 is not a usable seller file; a page displaying the right text with status 404 is not a successful file fetch either. Compare both the response headers and the body. Test HTTP and HTTPS separately: Google attempts both, and an HTTPS error can affect entries even when HTTP serves a file. Use the personalized snippet from the intended account without publishing its identifier in a public support request.
Preserve a result that support can act on
If the listing changed recently, record that change separately from the file edit. The setup guide allows up to 24 hours for detecting a Google Play developer-website change and describes a “Check for updates” action. Its crawlability page also notes that reflected updates can take longer, particularly with low request activity. Treat these as documented timing considerations, not a promise that every verification warning disappears after one day.
Make one scoped correction, preserve the served response, then recheck the account's observed status. Escalate with the app/store identity, relevant URLs, redacted response evidence and timeline if the same failure persists. Do not remove valid authorizations merely to clear a warning. Successful verification resolves an authorization/discovery check; it does not establish valid traffic, viewability or paid delivery. Continue those investigations through the AdMob invalid-traffic guide and the delivery-verification workflow, as applicable.
When authorization succeeds but the app stays Getting ready, use the AdMob readiness and request-evidence audit. Preserve the account message, store linkage, app-review status and controlled SDK result instead of repeatedly editing a file that already verifies.
A repeatable validation checklist#
1. Identify the exact property
Record the website domain or app/store identity. Identify the entity that owns it and the applicable manager, if any. Avoid substituting a corporate parent domain for the actual advertised inventory without explaining the relationship.
2. Fetch and preserve current declarations
Save ads.txt or app-ads.txt and each relevant sellers.json response with timestamps and response metadata. Distinguish an HTTP failure or parser error from a successful fetch in which a seller ID is absent.
“Could not check” and “not found in the fetched file” are different results. Retry technical failures through an agreed process, and do not silently treat them as verified matches.
3. Compare exact account identities
Match system domains and seller IDs. Check seller type, seller business domain, account controller, and owner/manager context. Keep a reason for each unresolved mismatch.
IAB Tech Lab's implementation article explains why seller-domain linkage matters when the owned property and business domain differ or monetization is delegated.
4. Reconcile a transaction sample
Use authorized bid samples for the relevant property, account, geography, and time. Resolve the node identities and assess the declared path under the applicable standard. Public files alone cannot show which route the campaign actually bought.
5. Make a scoped decision
Correct a confirmed inaccurate declaration, seek missing evidence, or remove authorization no longer intended. Record owner, rationale, exact diff, and rollback plan. Buyers can separately apply their own documented policy to unresolved supply.
6. Verify after the change
Fetch the served file, confirm seller metadata where applicable, and check that the intended transaction path and buyer validation status reflect the change. Keep dated before-and-after evidence. A saved local file or closed ticket is not confirmation that the public declaration changed.
Copyable partner clarification request#
Subject: Authorization and seller identity review for [property]

Property / app identity:
Observed file URL and fetch timestamp:
Advertising system:
Seller ID, preserved exactly:
ads.txt relationship:
sellers.json name / domain / type:
OWNERDOMAIN / MANAGERDOMAIN and country, if applicable:
Observed schain and transaction timestamp, via secure channel:

Please confirm:
1. Which entity controls this account and receives payment?
2. Which agreement authorizes this inventory relationship?
3. Which current specification scenario represents the path?
4. Why do these public declarations differ, if applicable?
5. Is the account active, and which integration or deals use it?
6. Which declaration needs changing, by whom, and when?
7. How will we verify the correction after buyer refresh?

Proposed change / review owner / rollback reference:
For a partner handover, compare Manage Account and Manage Inventory arrangements separately from seller authorization. For suspicious creative behavior, use the publisher malicious-ad investigation checklist; an authorized seller record alone does not establish creative safety.
Frequently asked questions#
Does DIRECT always mean the shortest possible supply path?
DIRECT is an account-relationship value. A manager can be the most direct practical route to inventory while the exchange's account relationship remains RESELLER. Review the owner, manager, seller identity, and documented path together.
For a DV360 buyer’s direct-only requirement, audit the effective authorized-seller setting, bought seller states and separate chain evidence. A relationship filter and a numerical path rule need different acceptance checks.
Do MANAGERDOMAIN and INVENTORYPARTNERDOMAIN resolve the same warning?
No. MANAGERDOMAIN supplies context about primary or exclusive monetization management; it does not automatically validate a DIRECT versus INTERMEDIARY mismatch. INVENTORYPARTNERDOMAIN represents an inventory-sharing referral and must join the applicable request and partner authorization file. Establish the account controller, selling rights and payment relationships before correcting either declaration.
Is an unfamiliar sellers.json entry proof of spoofing?
No. It is a claim requiring investigation. Preserve the record, check your own partner history, ask the publishing system to identify the account, and reconcile authorization and transaction evidence before attributing intent.
Should every RESELLER line be removed?
No universal rule follows from the label. Decide which authorizations you intend to grant, investigate unknown entries, and evaluate active commercial dependencies. Remove obsolete or incorrect authorizations with a documented change and verification plan.
Is Firebase Hosting itself an invalid location for app-ads.txt?
No. Google documents support for Firebase Hosting, including web.app and firebaseapp.com. Verify the public store link, the exact crawl URL in AdMob, the final file response and the account's seller snippet. A supported hosting option does not guarantee that those individual checks pass.
Do valid ads.txt and sellers.json records prove good impressions?
No. They support authorization and identity checks. Delivery, invalid traffic, viewability, geographic accuracy, and business outcomes remain separate measurements.
Turn a warning into an evidence-backed decision#
The useful result is a clear account-level record: the property, authorized relationship, declared seller identity, actual observed path, unresolved questions, and correction owner. That record is more valuable than a cleaner-looking score with no explanation.
Learn about AdProof, explore verification solutions, or discuss a supply-path review. Bring the specific account and transaction evidence so the required scope can be assessed without assuming what public files alone prove.
Sources and research notes#
Originally researched on 25 October 2026. AdMob discovery and crawlability references reviewed on 27 October 2026. Inventory-sharing authorization references reviewed on 28 October 2026; the linked integration question was posted in December 2025 and is retained as an evergreen workflow gap, not a fresh incident. Technical references are the IAB Tech Lab ads.txt, sellers.json, SupplyChain specifications and implementation resources linked at the relevant sections, plus Google's seller-information documentation for its platform-specific example. Forum threads supply the original questions and are not treated as validated findings about named companies. Example domains and account IDs are hypothetical. Commercial cleanup and investigation steps are editorial recommendations, not certification, legal conclusions, or claims of an AdProof automated validation feature.
Compare authorization with the reported seller path
ads.txt, sellers.json and a supply-chain record describe different parts of a transaction. Discuss the specific seller evidence available.
Discuss measurement optionsA short inquiry to scope relevant options; no campaign access is needed.