
- Published
- Oct 28, 2026
- Updated
- Nov 12, 2026
- Reading time
- 12 min read
GA4 Payment Referrals: Audit a Hosted Checkout Journey
Diagnose GA4 payment referrals, cross-domain identity gaps and missing purchases with a practical hosted-checkout test and an order-level evidence checklist.
In this guide (10 sections)
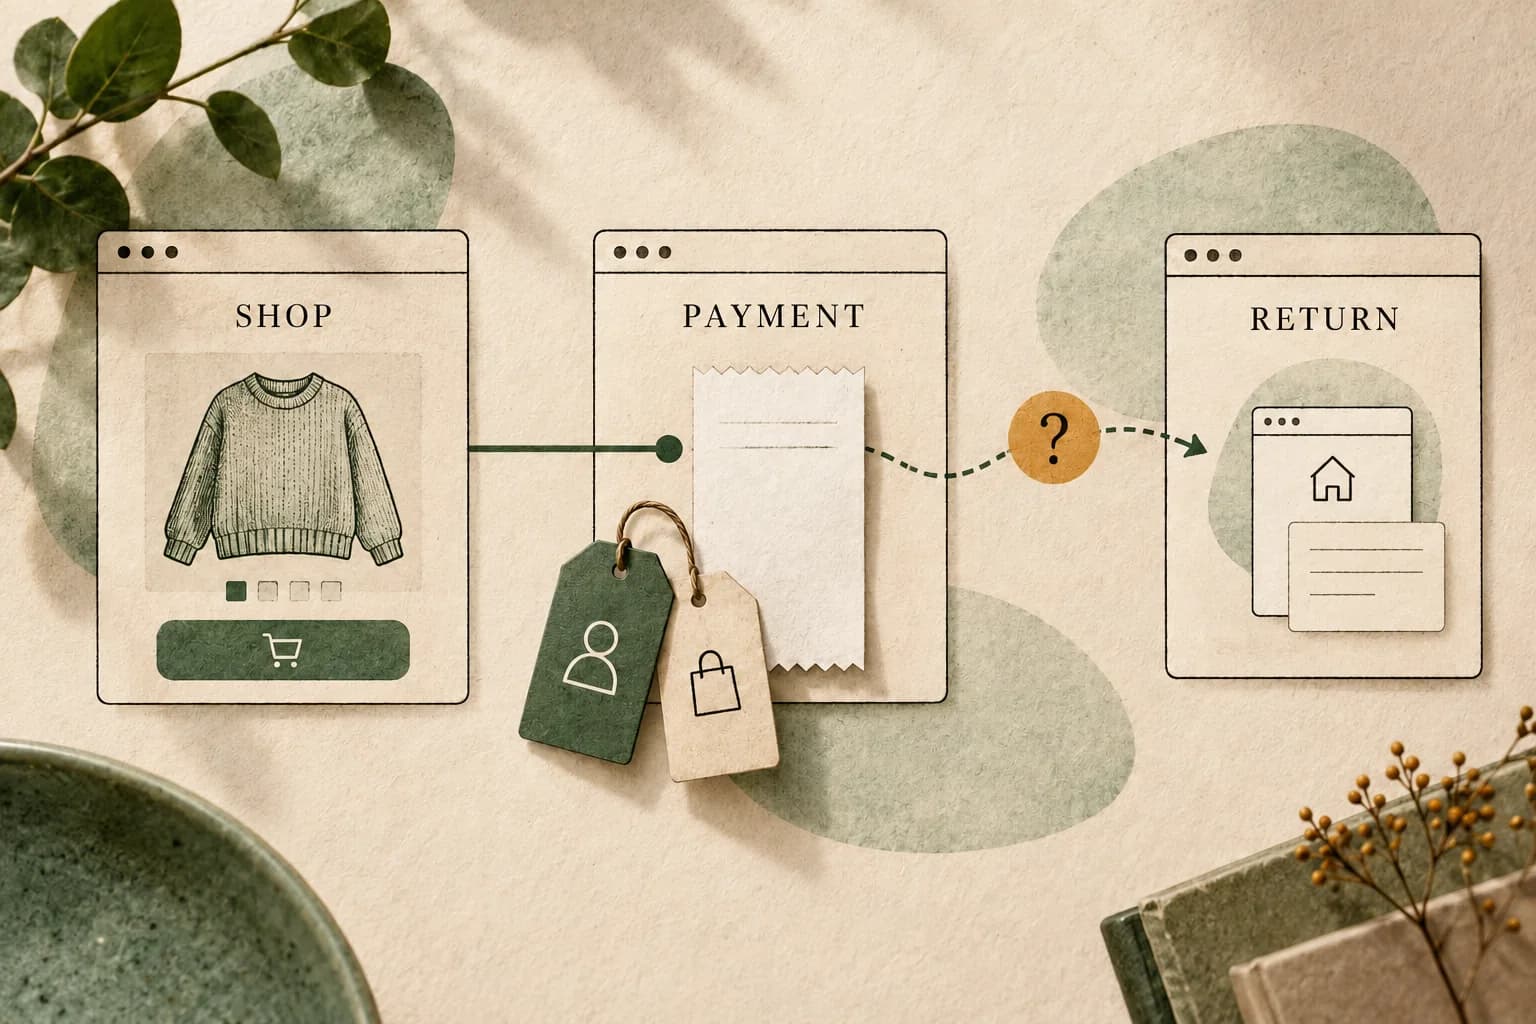
If GA4 credits your payment provider for purchases, start by separating three questions: should that domain be treated as an acquisition source, does the returning browser retain the expected measurement context, and was the purchase collected at all? An unwanted-referral setting addresses the first question. Cross-domain measurement may address the second when the participating sites support it. Neither setting creates an absent purchase event.
This matters when your shop sends a buyer to a hosted checkout you cannot tag. A tidy referral report can coexist with missing orders or broken attribution. Follow one authorized test order through the complete trip before changing the configuration.
The problem comes from a real Google Tag Manager community question, posted on 7 October 2026, with a substantive reply visible from 19 October when reviewed. The shop owner reports purchases attributed to a payment provider and asks whether cross-domain linking helps without control of that middle domain. Replies suggest different mechanisms but do not establish which configuration fixes that particular shop. This guide develops the missing diagnostic sequence; it does not claim a confirmed outcome for the poster.
Identify which checkout problem you actually have#
Write down the observable failure before choosing a setting.
| Observation | First investigation | Evidence that would help |
|---|---|---|
| A payment domain appears as a purchase source | Acquisition classification and the report's dimension scope | Exact source dimension, return referrer and current unwanted-referral rules |
| The returning visit appears disconnected | Browser identity and session context | Consented test identifiers and timestamps before departure and after return |
| An accepted order has no purchase event | Collection path | Order confirmation, return-page execution and outgoing purchase request |
| One accepted order appears repeatedly | Trigger ownership and repeat handling | Transaction identifier, senders and reload/retry behavior |
| Revenue differs despite matching order IDs | Value definition and reporting population | Item totals, currency, taxes, shipping, refunds and date boundaries |
Several rows can apply at once. Avoid declaring success because the provider disappears from one chart. Choose a separate pass condition for each symptom you are investigating.
If the problem begins earlier, with ad clicks that never become measured website visits, use the Google Ads clicks versus GA4 sessions guide. This article starts at the checkout boundary rather than treating all acquisition discrepancies as one problem.
Trace the hosted checkout journey
Record referral classification, measurement context and purchase collection separately.
Use the tracking QA checklistOpens a practical guide. No email required.
Map what you control#
Draw the real journey using hostnames and navigation steps: shop, checkout, any authentication or payment redirect, confirmation page and later order-status page. Record whether each step is a full navigation, a new tab or an embedded frame. Do not assume an iframe and a top-level redirect expose the same integration options.
For an embedded booking widget, audit the supported success signal and cross-frame receiver before changing referral settings. Establish which document owns the event and sender, and verify the parent handoff separately from business acceptance and the outgoing GA4 request.
For each hostname, answer these questions:
- Can your team install and maintain the approved Google tag there?
- Does the provider offer a documented analytics integration for this checkout product and plan?
- Can you configure the success and cancellation return destinations?
- Which system confirms that the order reached your agreed purchase state?
- What happens if payment succeeds and the browser never returns?
Ask the provider about these capabilities individually. A configurable success URL does not establish permission to run arbitrary scripts on its checkout. A webhook option does not establish that a complete analytics implementation already exists.
Keep a minimal private test sheet with a non-personal test order reference and the expected journey. Avoid putting customer names, email addresses, payment details or access tokens into diagnostic URLs, screenshots or analytics parameters. Redact evidence before sharing it with an implementation partner.
Establish a comparable reporting baseline#
Save the report name, property, web stream, date range, time zone, filters and exact dimensions before making a change. Record whether the metric is purchase events, ecommerce purchases, key-event credit or revenue. A screenshot labeled simply “source” is too ambiguous for a later comparison.
Google distinguishes first-user, session and event acquisition scopes. First-user dimensions describe initial acquisition; session dimensions describe session acquisition; event-scoped traffic dimensions support attribution of key events. These can answer different questions for the same buyer. Use the official explanation of traffic-source scopes to select the comparison that matches your question.
For example, if your concern is the source of sessions containing purchases, keep the session-scoped dimension consistent. If your concern is credit assigned to purchase key events, record the applicable attribution settings too. Do not treat a difference between those two views as proof that the checkout integration is broken.
Separate a controlled journey check from an aggregate business comparison. The former helps locate a failure. The latter needs a comparable order population and adequate processing time. One successful test cannot establish complete collection across every browser, payment route or consent choice.
Use unwanted referrals for the classification problem#
Google explicitly identifies third-party payment processors as a common unwanted-referral use case. In the appropriate web stream, the current path is Configure tag settings → Show all → List unwanted referrals. Review the actual return domains and matching rules before adding a condition. Google's unwanted-referrals documentation explains that matching events receive an instruction to ignore the referrer for attribution.
Treat this as a scoped classification change. It does not install a tag on the provider's pages, connect two independently created browser identities or manufacture an order event. Do not exclude every referral domain to make a dashboard look cleaner: legitimate acquisition sources could disappear from the analysis.
Record the setting and activation time, then repeat the authorized journey. Existing attribution history can still affect later reports; the same documentation explains why previously acquired users may continue to appear under an excluded domain. Do not promise that saving the setting will rewrite historical attribution or immediately remove every occurrence.
Use cross-domain measurement only where the journey supports it#
Google's standard setup requires the same Google tag ID from the same web stream on participating pages. Its linker carries measurement identifiers through the _gl URL parameter during supported navigation. The cross-domain setup documentation also warns that redirects can remove that parameter and describes inspecting the destination URL and network requests.
That makes control of the checkout integration a practical decision point. If the provider does not support your tag or an appropriate integration, adding its hostname to a domain list alone does not demonstrate a measured checkout journey. Ask for the provider's supported approach rather than improvising identifiers into arbitrary URL fields.
Where supported, test the actual link or form, including intermediate redirects. Inspect before-and-after measurement context under the approved consent configuration. Seeing _gl is a useful transport check; confirm the receiving implementation behaves as intended as well. A parameter present in an address bar is not, by itself, a complete attribution test.
Also test the return to your original shop independently. Returning to the same shop in the same browser may retain its existing context without measuring activity inside the provider. That observation still leaves provider-page visibility and purchase collection as separate questions.
Inspect session context without applying old assumptions#
For a permitted, consented diagnostic journey, note the available client context, session identifier and event timestamps before checkout and after return. Compare them with the known route and elapsed time. Keep this evidence restricted; identifiers are diagnostics, not a substitute for an approved identity policy.
GA4 starts a session when a page or screen is viewed without an active session; its default inactivity timeout is 30 minutes. Its documentation also describes associating session IDs with events and warns that a session ID alone is not a globally unique session key. See About Analytics sessions.
Consequently, a later return may legitimately need separate investigation from an immediate return. Do not assume that every different session identifier proves a failed linker, or that a matching client identifier proves correct purchase credit. Preserve the observed facts and test the relevant reporting question.
Repeat the journey using the consent states your organization supports. Do not force a granted state to obtain prettier continuity evidence. Record a consent-dependent limitation as such rather than silently classifying it as a technical failure or trying to bypass it.
Confirm the purchase path, including no return#
Google's ecommerce implementation guide describes sending a purchase event with item data, using a transaction identifier, and providing event-level currency when sending value. A thank-you page view alone does not establish that your implementation sent those ecommerce fields.
Define your business's accepted purchase state with the commerce owner. Then trace where that state becomes available to the configured event sender. Inspect the outgoing event and the receiving evidence, not just a tag's “fired” label. Check that the destination is the intended property and that the value follows a documented policy for discounts, taxes and shipping.
Test reopening the confirmation page and retrying the route. Keep the same test transaction reference for the same order so repeat behavior can be reviewed. Do not fix duplicates by inventing a fresh order ID on every page load. If several plugins, browser tags or server integrations can send the purchase, identify their ownership before adding another sender.
Now test the missing-return case in an approved sandbox or test workflow. If the only purchase sender executes on your shop's return page, a buyer who never loads that page cannot execute that sender. Referral exclusion cannot resolve that architectural dependency.
Ask whether the provider offers a supported order-confirmation integration or notification path that your team can implement appropriately. Assess consent handling, identifier availability, transaction ownership, duplicate prevention and destination validation together. A generic recommendation to “use server-side tracking” does not answer those implementation questions, and moving a sender does not guarantee attribution recovery. This guide does not prescribe a provider-specific integration without its current documentation.
Add a Shopify app-pixel and consent check
A Google Analytics Community question opened October 11, 2026 reports 33 Shopify orders and 25 GA4 transactions for October 4–10. The author says several missing paid orders used Vipps and includes one refunded test order. Those are the poster's observations, not a verified cause. A commenter on November 10 hypothesized a consent app or external-payment return-path issue; the comment's timezone is not exposed, and the thread does not prove that diagnosis. Read the original question.
Shopify documents app pixels under Settings → Customer events and provides Pixel Helper to test whether a selected app pixel receives events. Its documentation distinguishes web pixels from server pixels: a server path may transmit through the app owner's server without relying on the buyer's return-page browser, but Shopify's privacy and consent settings still apply. Do not infer that a particular app sends a server event to GA4; verify the app, event, destination and order reference in its own documentation and test evidence. Shopify app pixels · GA4 ecommerce validation.
For a Shopify store, extend the existing order trace:
- Align the comparison population, date boundary, timezone, refunds/cancellations and test-order treatment before comparing totals.
- Inventory the app pixels and owners in Customer events. A theme tag, app pixel, checkout extension and server pixel are different senders.
- Use Pixel Helper on an authorized test to check whether
checkout_completedreaches the selected app pixel. Record the consent choice and any waiting state; do not disable privacy controls to make a test pass. - If the app owner documents a server pixel, inspect it separately from the browser path. Verify the event source, destination and order reference. A transmission does not prove GA4 receipt, correct identity or advertising attribution.
- In GA4 DebugView or another approved validation view, confirm
purchaseand itstransaction_id, currency and value. Check whether another integration also emits the same order. - Repeat for the payment methods in scope. One aggregate difference does not establish that a payment method, consent app or checkout extension caused it.
The reported aggregate difference is eight (33 stated Shopify orders minus 25 GA4 transactions), and 8 / 33 = 24.2% relative to the reported Shopify total. This describes only those poster-reported counts. It does not identify eight individually reconciled missing orders, establish a GA4 error rate, or prove a cause or loss.
| Observation | Supports | Does not establish |
|---|---|---|
| Shopify order exists | The commerce system recorded the order | GA4 collected a purchase or Ads credited it |
| Pixel Helper sees an app-pixel event | The selected pixel received the event in the tested browser path | GA4 accepted it or other payment/consent paths behave the same |
| Server pixel transmits an event | A server-side transmission occurred | Consent eligibility, correct transaction ID, GA4 processing or campaign attribution |
GA4 DebugView shows purchase | GA4 received the tested event and visible parameters | Production completeness or attributed credit |
| Aggregate totals differ | The populations or collection/reporting paths need reconciliation | Which order, app, consent state or payment flow caused the difference |
Worked example: three different failures in one checkout#
The following is hypothetical. It is a diagnostic exercise, not an AdProof customer result or an estimate of typical checkout loss.
A fashion retailer runs three authorized sandbox orders under the same documented test consent state. All use the same shop and hosted checkout route. The team retains one private test reference per order.
| Test order | Commerce evidence | Browser evidence | Investigation |
|---|---|---|---|
| A | Accepted order | Returns; one purchase request; provider shown in the selected acquisition view | Check referral rules and that view's scope |
| B | Accepted order | Returns after a long delay; changed session context | Check elapsed inactivity and attribution context before diagnosing continuity |
| C | Accepted order | Buyer closes the provider page; shop return page never loads; its purchase sender never runs | Review the return-dependent collection design |
Suppose all three orders are eligible for this deliberately narrow exercise, but only A and B produce an observed purchase request from the tested sender. Its observed coverage is 2 observed orders ÷ 3 eligible test orders = 66.7%. That is a three-order test result, not a production conversion rate. It says nothing about revenue value accuracy, processed GA4 purchases or which channel deserves credit.
Changing an unwanted-referral rule might address A's classification after validation. It does not cause C's missing page to run. Extending a session timeout without understanding B would likewise avoid answering the underlying question. Assign each finding its own owner and acceptance test.
Keep a checkout evidence packet#
Retain the journey map, supported integration references, configuration version, test time zone, consent state, redacted order reference, event payload fields and report selection. State exactly which paths passed and which remain untested. The broader marketing tracking QA checklist provides a repeatable release process for preserving that evidence.
For a production reconciliation, first align order eligibility: payment state, cancellations, refunds, currency, purchase timestamp, reporting cutoffs and permitted collection. Compare accepted-order identifiers with observed purchase identifiers before arguing about channel totals. Preserve unexplained records rather than forcing aggregate counts to match.
The same discipline applies upstream, but the counting unit changes. Our anonymized fashion-retail duplicate-counting case study concerns ad-impression reconciliation. It is not evidence of GA4 purchase recovery, checkout revenue or additional sales.
If you also need to examine campaign delivery, request an AdProof demo to discuss a separately scoped review of supported ad-measurement evidence. Bring the campaign, dates, environments and counting question. Keep that delivery review distinct from the checkout changes owned by your commerce and analytics teams.
Frequently asked questions#
Will excluding the payment provider fix old GA4 reports?
Do not assume a historical rewrite. Save the configuration change time and validate subsequent eligible journeys. Existing attribution history can continue to affect later reporting, so an excluded domain remaining in a report is not enough to diagnose a failed configuration.
Can cross-domain measurement work if I cannot tag the checkout?
The standard Google setup requires participating pages to use the same tag ID and web stream. Check for a documented provider integration. A domain-list entry alone does not establish tracking on a page you cannot instrument, and the return to your shop needs its own test.
Is a thank-you page visit enough to count a purchase?
It can be a useful execution location when your design verifies the appropriate order state, but the page visit is not the ecommerce event itself. Verify the configured purchase sender, transaction reference, relevant fields, repeat behavior and receiving destination.
Why can orders still differ after referrals look correct?
Because attribution classification and collection coverage answer different questions. Investigate non-returning buyers, sender failures, duplicates, consent-dependent coverage, value policies and reporting boundaries. Reconcile individual eligible order references before interpreting a change in an aggregate source chart.
A hosted-checkout collection audit does not settle campaign credit. For Meta and store reporting, compare the order cohort, received events and attribution views separately before changing tracking or budgets.
Trace the hosted checkout journey
Record referral classification, measurement context and purchase collection separately.
Use the tracking QA checklistOpens a practical guide. No email required.