
- Published
- Oct 31, 2026
- Updated
- Nov 4, 2026
- Reading time
- 10 min read
Multiple VAST Pixels: Audit Recipients Without Double Counting
Debug multiple VAST tracking pixels with event URI lists, wrapper provenance, sender ownership and receiver checks that keep requests separate from exposures.
In this guide (11 sections)
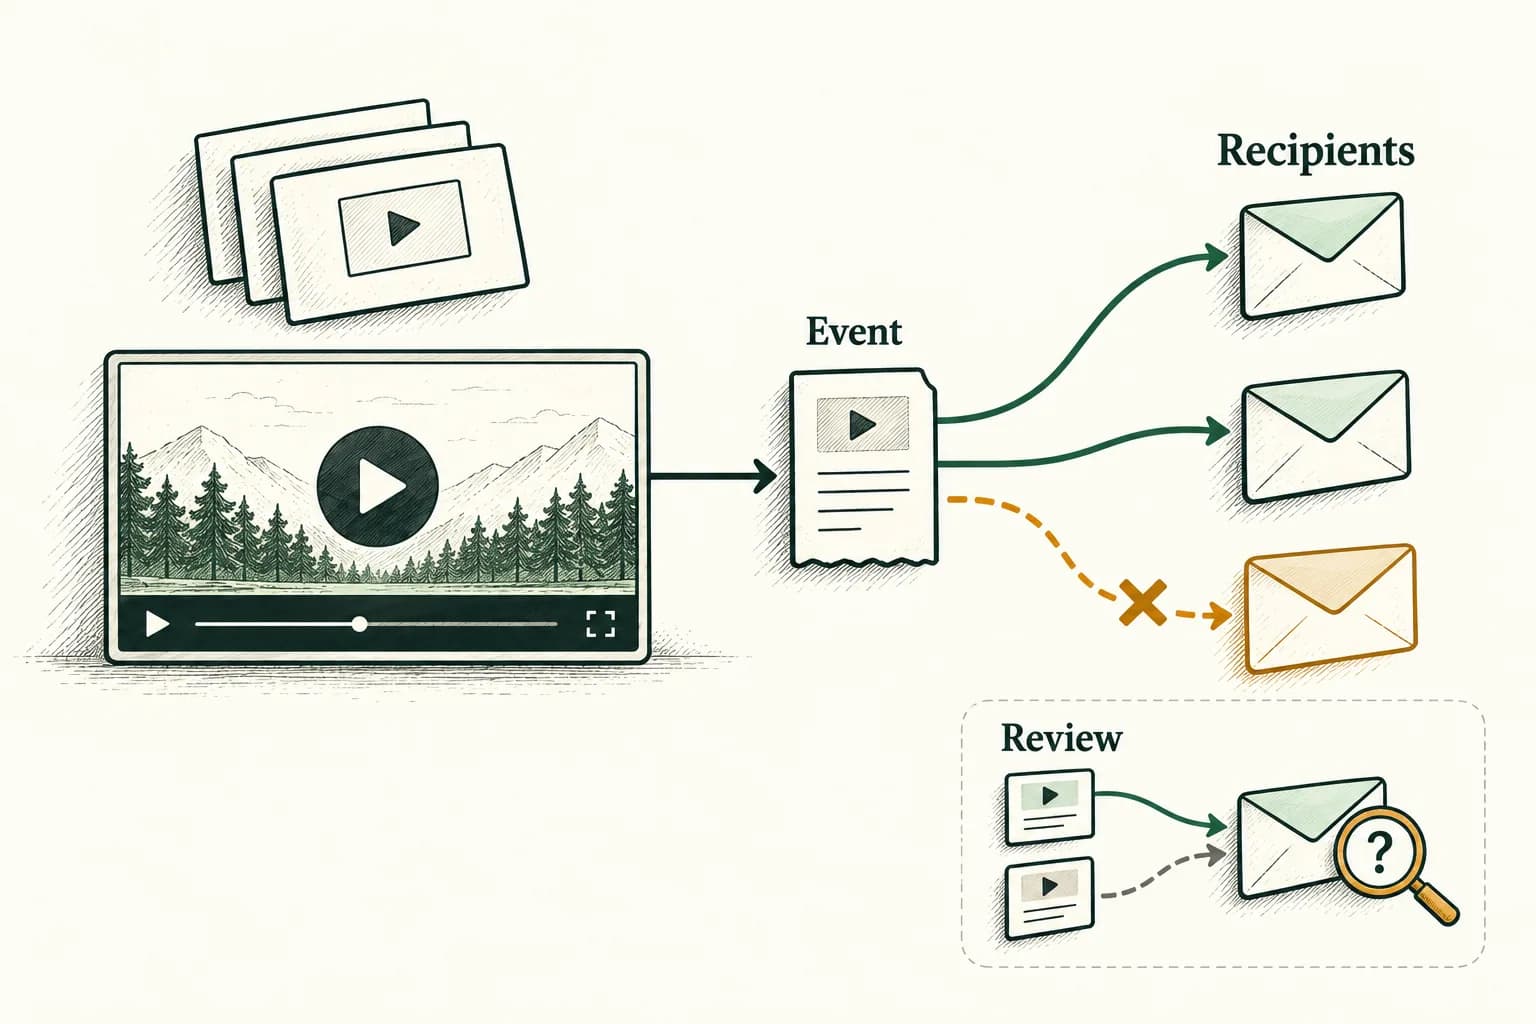
VAST can notify several recipients about one playback event. Represent each intended event URI separately, preserve the applicable wrapper and inline reporting obligations, and verify who sends them. Three legitimate recipients do not mean three ad exposures. Two independent senders reporting the same obligation are a different problem.
If your integration combines ads from differently versioned responses, first validate the assembled response and its output contract before auditing each recipient.
For a manual Android IMA adapter, trace player progress and callback ownership before diagnosing a missing recipient.
An older question about multiple VAST pixels asks how to send start and skip notifications to an operator and a client. The author tried separate nodes and a comma-separated value, then substituted progress events. A later comment asks whether multiple impression nodes work too. The discussion leaves a useful gap: correct structure is only the beginning of an end-to-end test.
A second older question about wrapper click tracking reports that navigation works while an outer wrapper's notification is missing. Its replies suggest different causes. None establishes the behavior of every current SDK, so this guide uses current primary references and a reproducible recipient audit rather than adopting an old workaround.
Establish the small set of format rules first#
IAB Tech Lab's VAST 4.3 reference provides these relevant rules:
- Section 3.14 allows multiple
Trackingentries for the same event, with one event URI per entry. - Section 3.4.4 calls for the inline and preceding wrappers' impression URIs to be triggered when that ad's impression occurs, as close together as possible.
- Section 3.10 distinguishes the navigation destination,
ClickThrough, fromClickTrackingnotifications to interested parties. - Section 2.3.5.2 gives the inline click-through precedence; if absent, the closest calling wrapper's click-through is favored.
Those are separate contracts. An inline navigation choice does not mean that every outer reporting destination should be discarded. Likewise, a parser that finds one URI has not necessarily retained every intended recipient.
This partial illustration shows two start recipients. It is not a complete playable VAST document:
<TrackingEvents>
  <Tracking event="start"><![CDATA[https://example.org/operator/start]]></Tracking>
  <Tracking event="start"><![CDATA[https://example.net/client/start]]></Tracking>
</TrackingEvents>
A comma-separated string is not this list of elements. If the correct structure still fails, investigate the delivered response and runtime path instead of changing the meaning of the event.
Map each VAST tracking obligation.
Use the checklist to record intended event URIs and which system sends them.
Use the tracking QA checklistOpens a practical guide. No email required.
Inventory reporting obligations before investigating counts#
Choose one authorized playback attempt with a known creative and actual response. Give it an internal trace identifier and retain the relevant request time and timezone. Map its expected reporting destinations without treating each destination as another impression.
Build a table with one row per reporting obligation:
| Field | Why it matters |
|---|---|
| Response origin | Identifies inline, wrapper or separate configuration |
| Creative/component | Keeps linear, companion and other interactions apart |
| Event | Defines the observation that should trigger reporting |
| Intended recipient | Identifies who should receive the notification |
| Responsible sender | Establishes SDK, player, service or application ownership |
| Runtime result | Links the event to an actual outgoing request |
| Receiver result | Shows receipt and later reporting treatment separately |
Keep the original references in restricted evidence. Signed addresses, tokens and personal identifiers should not appear in a public troubleshooting packet. Sanitized references are usually enough to explain where the chain stopped.
Ask the ad-serving owner which URLs were intentionally configured. An address that resembles another one may serve a different reporting purpose. Conversely, adding a URL manually because a dashboard is quiet can introduce another sender without repairing the original failure.
Inspect the response that this playback actually received#
Capture the initial response and each resolved wrapper through the final inline response. Retain the order, response outcome and relevant creative/component association. Opening the same tag later can return a different creative and is not a reconstruction of the failed attempt.
Compare the configured recipient inventory with the returned inventory. If a URL is absent from the outgoing response, identify the serving or configuration boundary that omitted it. If it is present, continue into parsing and dispatch. This separates a configuration issue from a player issue before anyone changes both.
Check parser cardinality. A diagnostic question is whether a collection of same-event nodes was accidentally reduced to a single value keyed only by event name. If the implementation stores one start value, inspect whether a later entry overwrote an earlier recipient. This is a testable hypothesis, not an assertion about a particular SDK.
Keep source provenance while combining the applicable records. A flattened list without its wrapper/component context can make later support work unnecessarily difficult. Preserve the original responses even if a normalized recipient list is useful for testing.
For failures resolving wrappers or fetching media, use the separate VAST errors and timeouts workflow. A failed creative path and a successful playback with one silent recipient need different investigations.
Preserve the event rather than substituting a timer#
The original multiple-pixel question tried progress offsets as a substitute. That changes the question being measured. Reaching a chosen time is not the same observation as a user activating skip, and an approximate timer is not proof that a start event was delivered to every recipient.
Google's Campaign Manager third-party URL reference documents multiple URLs of a given type and distinguishes start, quartiles, completion, skip and progress. Use the type intended by the measurement agreement, then inspect whether its actual trigger occurred.
For an event that did not occur in a test, mark the branch unexercised. Request an appropriate authorized fixture or interaction before claiming it works. Do not manufacture a skip or completion merely to see its endpoint appear in the network panel.
Keep optional progress measurement as its own agreed observation when required. Correcting a missing start recipient should not silently redefine the client's start metric as “one second later.” That can hide the integration issue while making reports harder to compare.
Give one component responsibility for each dispatch#
A common diagnostic branch is that the SDK already handles a VAST URL while application code also sends it from an SDK event listener. Trace both initiators before deciding that the duplicate belongs in the receiver's deduplication layer.
For IMA HTML5, its AdEvent reference describes IMPRESSION as the impression URL having been pinged. Receiving that notification is not an instruction to ping the same VAST URL again. The exact integration still needs inspection; an application listener can legitimately collect separate authorized telemetry without duplicating the ad-reporting obligation.
Compare the sender plan with network initiators and runtime callbacks. A second request could also follow a retry, repeated callback registration or actual repeat playback. Record enough context to distinguish those possibilities rather than equating every repetition with fraud.
Do not remove an intended recipient to make counts look cleaner. Correct an evidenced duplicate path under the integration owner's supported contract, then repeat the same test. Keep retry and replay policy explicit; there is no useful universal rule that every repeated URL is a new impression or that every repeated URL must be suppressed forever.
Treat click navigation and click notifications separately#
For an authorized click test, record the interface that was activated, the chosen destination, the reporting requests and whether the landing page actually loaded. These are distinct observations with different owners.
For IMA HTML5 custom controls, verify current-ad custom click-element eligibility, placement and visibility before investigating the recipient path.
The wrapper-click question is useful because reaching the destination can coexist with missing notification evidence. Test the structure and relevant creative wrapper in the actual response. A selected navigation URL does not demonstrate receipt at an operator's click-reporting endpoint.
Also distinguish the linear ad's click from a companion, icon or another supported interaction. Do not put every click-like URL into one generic dispatcher. Record which component actually received the interaction and which contract governs its reporting.
Retain the native interaction result as well as the network trace. A test that manually opens a reporting address can establish endpoint behavior, but it cannot establish that the released player dispatched it on the intended click. It can also pollute measurement, so keep such endpoint checks explicitly authorized and separate from event acceptance.
Follow each recipient into its own report#
For each expected dispatch, record whether a request was attempted, the transport outcome and any authorized matching receiver record. Then confirm the report's event definition, date basis, timezone, filters and processing interval.
A transport response is not the same evidence as a processed reporting row. Likewise, a missing row does not identify whether the player failed to send, the recipient rejected the record or the report omitted it. Preserve the first missing boundary and send that question to the owner who can inspect it.
Keep recipients separate when comparing totals. Summing an operator's start count and a client's start count usually combines reports about overlapping playback, not independent reach. First establish their common population and counting policy.
Where a recipient cannot expose event-level evidence, state that limitation. Do not fill the blank by treating a browser event as proof of receiver acceptance, or by declaring all unjoined rows lost. The platform comparison guide explains why collection, processing and reporting scope need separate checks.
A hypothetical acceptance review with three recipients#
Hypothetical example only. Ten authorized ad starts each have three intended start recipients. The configured test therefore has thirty event-recipient reporting obligations, not thirty ad starts.
The reviewer assigns each obligation one initial status:
| Initial reporting status | Event-recipient obligations |
|---|---|
| Expected dispatch and receiver evidence matched | 24 |
| No outgoing dispatch evidenced | 4 |
| Outgoing dispatch observed; receiver match unresolved | 2 |
| Total | 30 |
The matched-evidence share is 24 / 30 = 80% of obligations. It is not a viewability or audience metric. The four missing dispatches and two unresolved receiver matches need different next actions.
Suppose application code also makes five additional requests to a recipient already handled by the SDK. Now the trace contains thirty-one outgoing requests: twenty-four matched, two unresolved and five extra. That total does not establish thirty-one starts, and it does not erase the four obligations without dispatch evidence.
The reviewer keeps the five extras in a separate sender investigation. A later reduction from thirty-one requests to twenty-six is not automatically a loss of legitimate exposures. Conversely, a higher request count after a change is not proof that every missing recipient was repaired.
These invented numbers describe one controlled test. They do not establish campaign-wide discrepancy, invalid traffic, refunds or savings.
Repeat an acceptance matrix before closing the handoff#
Use authorized fixtures and representative runtime versions. Exercise the same recipient inventory through these branches:
- Multiple same-event recipients in an inline response.
- An applicable wrapper recipient plus the inline recipient.
- Start and completion as separate observed events.
- A real supported interaction, with navigation and notification checked separately.
- A failed destination while other intended recipients remain observable.
- Repeated callbacks, retries or genuine replay under the documented policy.
Retain failed branches and unknowns. Confirm that the tested build is the released build and preserve the response used for each attempt. One inspector success should not become a universal claim about every player, app and server-side insertion path.
For server-side insertion, identify which component receives VAST and which one sends the notifications. Use the SSAI evidence guide for that provenance question. For MediaTailor metadata refreshes, use the separate client-tracking workflow; repeated metadata is not a fresh playback event.
Bring the recipient audit to the campaign review#
Send the implementation owner the actual response chain, recipient inventory, observed event, responsible senders, outgoing requests and available receiver records. State whether the first missing boundary is configuration, parsing, dispatch or reporting. That packet is more actionable than a screenshot labeled “pixels broken.”
If a VAST request fails alongside an application exception, separate timeout classification, runtime survival and response-body deadlines before increasing a limit.
For supported campaigns already sending relevant events to AdProof, prepare a campaign/date/timezone-scoped export of available delivery and video-stage evidence. Keep received rows, supported validity/duplicate-related measures and the runtime recipient inventory explicit. The export does not promise automatic access to every VAST response, SDK callback or third-party receiver.
The anonymized streaming-publisher case supplies reconciliation context. Discuss the available campaign evidence before converting a total of tracking requests into a claim about unique impressions or over-frequency.
Frequently asked questions#
Can one VAST event have more than one tracking recipient?
Yes. Use the appropriate separate event entries and preserve the applicable response context. Then verify the actual dispatch and receipt for each intended recipient.
Are three tracking requests always three impressions?
No. Several requests can notify different recipients about one event. Establish the exposure, event and recipient populations before counting or combining reports.
Should I fire a VAST pixel again when an SDK reports an impression?
First identify the existing sender. An SDK notification can follow its own dispatch; sending the same obligation again can create an additional path. Separate authorized application telemetry from VAST reporting.
Does a working click-through prove wrapper click tracking works?
No. Navigation and reporting are separate checks. Verify the actual interaction, response structure, outgoing notification and recipient evidence independently.
Map each VAST tracking obligation.
Use the checklist to record intended event URIs and which system sends them.
Use the tracking QA checklistOpens a practical guide. No email required.